Find the weaknesses attackers look for
Manual and automated offensive security testing built around the systems you operate and the audit you need to pass. Our in-house specialists work to established methodologies and report what matters in your environment.
Two connected attack surfaces
Applications and infrastructure often expose different paths to the same sensitive data. Start with one specialty or scope them together.
Application Penetration Testing
Web applications, APIs, and mobile apps tested individually or as one connected system. Aligned to OWASP WSTG, API Security Top 10, MASTG, and MASVS.
Explore application testingInfrastructure Penetration Testing
External perimeters, internal networks, and wireless environments assessed through realistic attacker scenarios aligned to OSSTMM, PTES, and NIST SP 800-115.
Explore infrastructure testingTesting shaped around the evidence you need
SOC 2 Type II
Technical evidence for the security criteria your auditor asks to see.
HIPAA
Testing that supports technical safeguard reviews for systems handling PHI.
PCI DSS
Segmentation and application testing aligned to applicable requirement 11 expectations.
NIST 800-53
Technical validation mapped to the control families relevant to your environment.
Need this mapped to your audit? Let’s talk scope
Cloud and OT/ICS testing
Cloud configurations and operational technology require environment-specific scoping. We assess cloud environments against relevant CIS Benchmarks and plan OT/ICS work around operational safety.
Technical depth behind every engagement
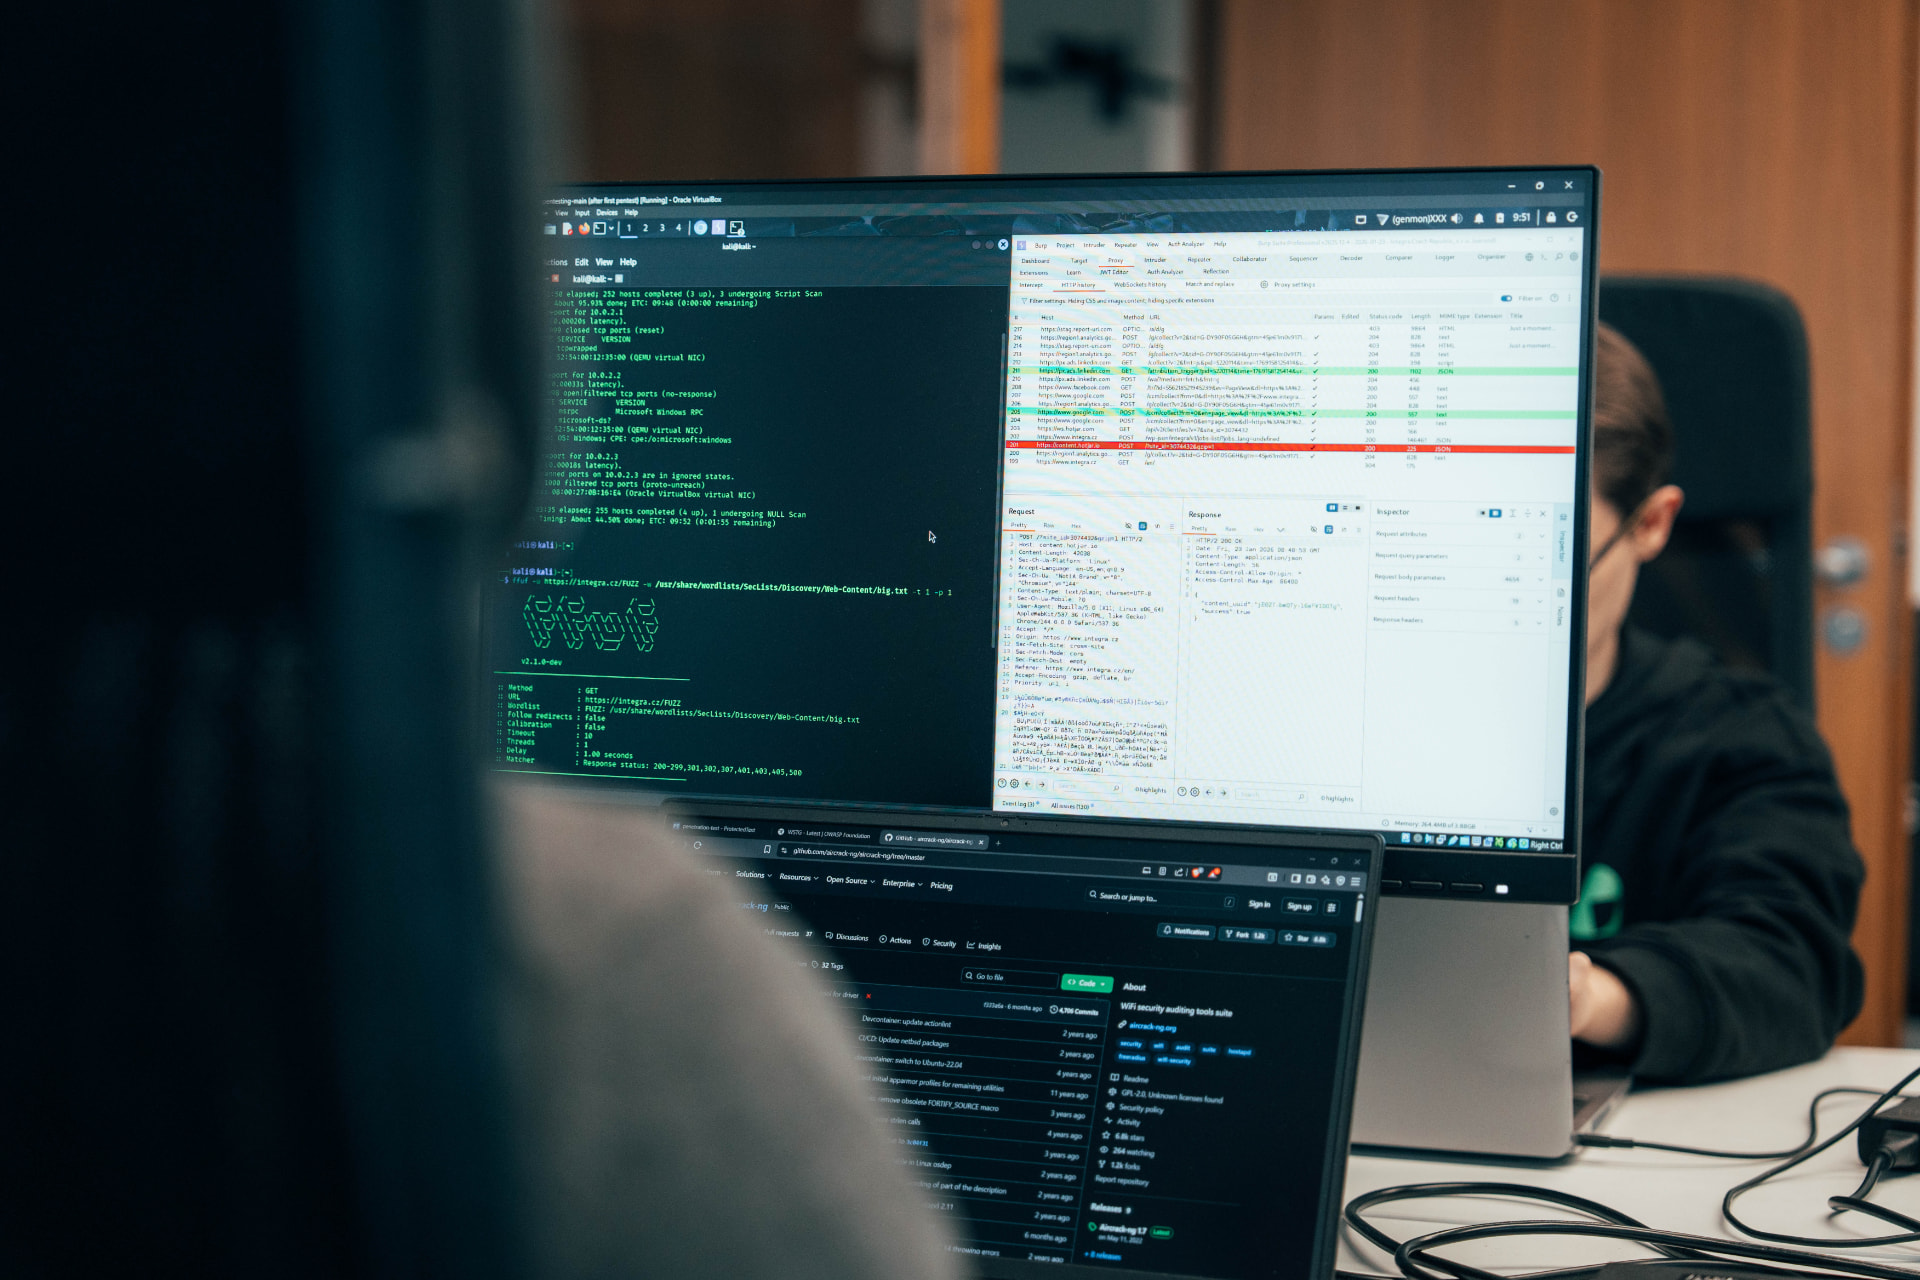
Our testers hold certifications including OSCP, OSWP, CRTO, CEH, and AWS Security Specialty, among others. Our in-house team delivers 200+ penetration tests annually across 9+ industry sectors.
The setup shown is used for controlled testing on INTEGRA-owned targets, never client environments without explicit authorization.
A partner that reports what matters
Technical depth is only useful if the people paying for it can act on it. We structure every engagement so the findings reach the right audience with the right level of detail.
- Reports engineers and executives can both actually use — technical detail for your team, plain-language summary for leadership
- Certified testers with internal peer review of every finding before it reaches you
- Methodology drawn from real attacker tradecraft: OWASP, OSSTMM, PTES, and MITRE ATT&CK
- A free scoping consultation before any commitment
- 200+ penetration tests delivered annually by our in-house team across 9+ industry sectors
A clear process from scope to retest
You know what is happening, who to contact, and when to expect each deliverable.
- 1
Scoping
We confirm targets, objectives, access levels, exclusions, and the compliance requirement the test supports.
- 2
Kickoff & rules of engagement
We agree communications, safety limits, test accounts, escalation contacts, and the incident process before testing begins.
- 3
Testing window
Our specialists combine manual techniques with automated tooling. Critical findings are reported immediately, not held for the final report.
- 4
Written report
Each finding includes evidence, remediation guidance, CVSS scoring, and a real-world exploitability assessment for your environment.
- 5
Follow-up consultation
A free session with our technical team explains the findings, business impact, and practical remediation options.
- 6
Retest
We verify completed fixes and document the result so you can show auditors and stakeholders what changed.
Know what you need tested? Scope it in a free 30-minute call
Frequently asked questions
Get a sample penetration test report
See the format, technical depth, and executive summary style before you commit.
Get a security assessment
Tell us what is in scope and which audit or business requirement the test needs to support.